नमस्ते दोस्तों!
स्वागत है The Easy Master पर!
आपने scaling के बारे में सीखा – vertical aur horizontal scaling। अब अगला important topic है – Load Balancing। जब aapke paas multiple servers hain (horizontal scaling), toh traffic ko unme distribute kaise karein? Kaise ensure karein ki koi server overload na ho aur koi idle na rahe?
Load balancer yahi kaam karta hai – yeh ek “traffic police” hai jo incoming requests ko healthy servers ke beech distribute karta hai।
Jab maine pehli baar load balancer seekha, toh mujhe lagta tha ki bas round robin hi kaafi hai। Lekin jab maine production system dekha – jaha servers की capacity alag thi, sticky sessions chahiye the, toh samajh aaya ki alag-alag algorithms ke alag use cases hote hain।
इस Load balancing tutorial Hindi mein main aapko sikhata hoon:
✅ Load balancer kya hai? – Types (Layer 4 vs Layer 7)
✅ Load balancing algorithms – Round Robin, Weighted Round Robin
✅ Hashing algorithms – IP Hash, Consistent Hashing
✅ Least Connections, Least Time – kab use karein
✅ Session persistence (Sticky sessions) – Kaise aur kyun
✅ Health checks – Failover kaise kaam karta hai
✅ Real-world examples – Nginx, HAProxy, AWS ALB
✅ Load balancer deployment – Active-passive vs active-active
✅ Common mistakes aur best practices
Chaliye load balancer ki duniya mein step rakhte hain! 🚦🚀
Table of Contents
1. Load Balancer Kya Hai? – Traffic Police of Servers
Load balancer ek device ya software hai jo incoming network traffic को multiple backend servers के बीच distribute karta hai।
Load balancer kyun use karein?
| Benefit | Explanation |
|---|---|
| High availability | Agar ek server fail ho jaaye, load balancer traffic को healthy servers pe bhejta hai |
| Scalability | Traffic बढ़ने पर aap easily servers add kar sakte ho; load balancer automatically unme traffic distribute karega |
| Performance | Requests evenly distribute hone se koi server overload nahi hota, response time low rehta hai |
| SSL termination | Load balancer HTTPS decrypt kar sakta hai, backend servers par load kam hota hai |
| Health checks | Regularly check karta hai ki server alive hai ya nahi |
Load balancer ke two main roles:
- Traffic distribution – requests ko servers me baantna
- Fault tolerance – unhealthy servers ko remove karna, traffic healthy servers pe bhejna
Simple analogy: Ek restaurant mein multiple counters hain (servers)। Load balancer ek “manager” hai jo naye aane wale customers (requests) को सबसे kam line wale counter pe bhejta है।
2. Load Balancer Types – Layer 4 vs Layer 7
Load balancer do types ke hote hain based on OSI model layers:
| Feature | Layer 4 Load Balancer | Layer 7 Load Balancer |
|---|---|---|
| Operates at | Transport layer (TCP/UDP) | Application layer (HTTP/HTTPS) |
| Decision based on | IP address, port number | URL, headers, cookies, content |
| Speed | Faster (less processing) | Slightly slower (inspects content) |
| Use case | Simple TCP/UDP traffic, high performance | Web traffic, API gateways, content-based routing |
| Examples | HAProxy (TCP mode), AWS NLB | NGINX, HAProxy (HTTP mode), AWS ALB |
Layer 4 load balancer example:
Client request → Load balancer sees destination port 80 → Forwards to any server in pool (doesn’t look at URL).
Layer 7 load balancer example:
Request for example.com/api → goes to API servers group.
Request for example.com/images → goes to image servers group.
Recommendation: Web applications (HTTP/HTTPS) ke liye Layer 7 load balancer use karein – more flexible। For high-performance TCP/UDP (database, game servers) Layer 4 sufficient।
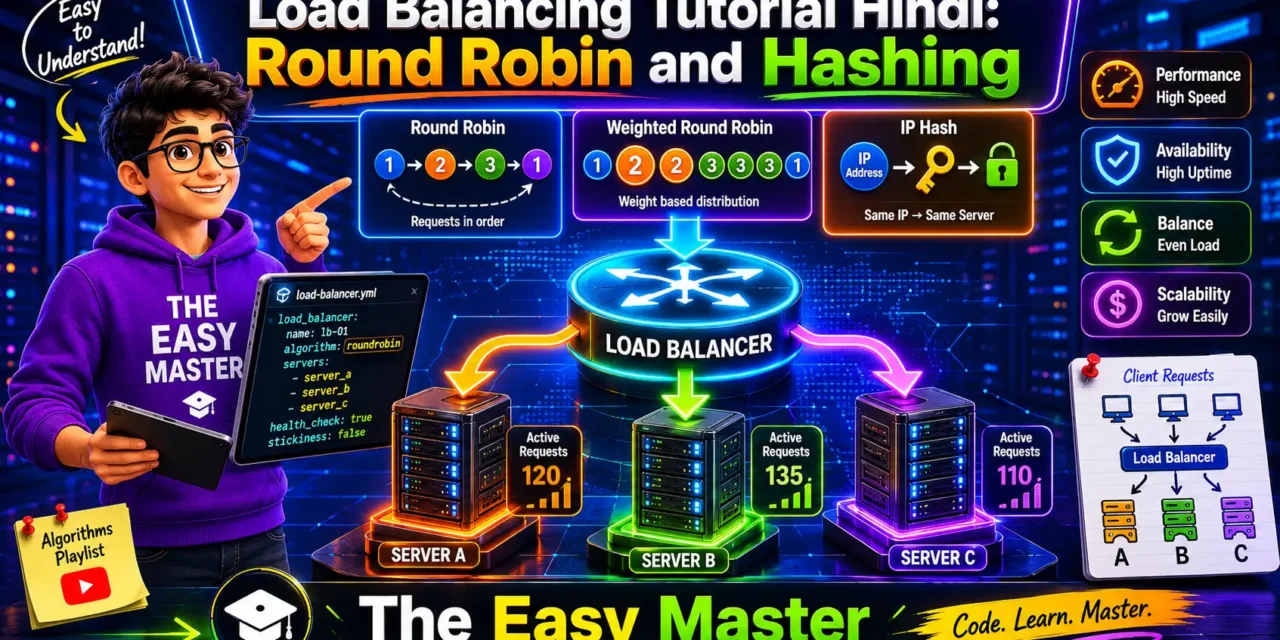
3. Load Balancing Algorithms – Round Robin & Weighted
3.1 Round Robin
Round robin सबसे simple algorithm है – requests को एक-एक करके sequentially servers में distribute kiya जाता है।
How it works:
- Servers list mein order maintain रखता है
- Har naye request ko next server bhejta है
- Last server के बाद first server par wapas aata है
Example with 3 servers (S1, S2, S3):
- Request 1 → S1
- Request 2 → S2
- Request 3 → S3
- Request 4 → S1
- Request 5 → S2 … and so on
Pros:
- Simple, easy to implement
- Works well if all servers have equal capacity
Cons:
- Sab servers equally capable hone chahiye – nahi toh slower server bottleneck ban sakta है
- Session persistence नहीं है (unless configured)
When to use: Homogeneous server pools, stateless applications।
3.2 Weighted Round Robin
Weighted round robin – servers ko weight assign karte ho जो unki capacity reflect karta hai। Higher weight वाले servers ko zyada requests milti hain।
Example:
- Server A: weight 5 (more powerful)
- Server B: weight 3
- Server C: weight 2
Out of 10 requests, A gets 5, B gets 3, C gets 2। Sequence bhi weight ke proportion mein distribute hoti है।
Use case: जब servers की capacity अलग-अलग हो – e.g., older servers (lower weight) और newer powerful servers (higher weight)।
Configuration example (HAProxy):
server server1 192.168.1.10:80 weight 3
server server2 192.168.1.11:80 weight 2
4. Hashing Algorithms – IP Hash and Consistent Hashing
Hashing algorithms ensure ki same client ke requests hamesha same server pe jaayein – useful for session persistence without sticky cookies।
4.1 IP Hash (Source IP Hash)
IP hash client ki IP address (or a portion) को hash karke server select karta hai।
How it works:hash(client_IP) % number_of_servers – result determines server index।
Example: Client IP 192.168.1.5 → hash value 12 → 12 % 3 = 0 → Server 0।
Pros:
- Simple, deterministic – same client always same server (good for caching, sessions)
- No overhead of cookies
Cons:
- Jika server pool size change ho (add/remove server), mapping changes drastically – cache miss storm (many clients go to different servers)
- Many clients behind same NAT (office, college) map to same server – load imbalance
When to use: Small-scale, server pool doesn’t change often, NAT not an issue।
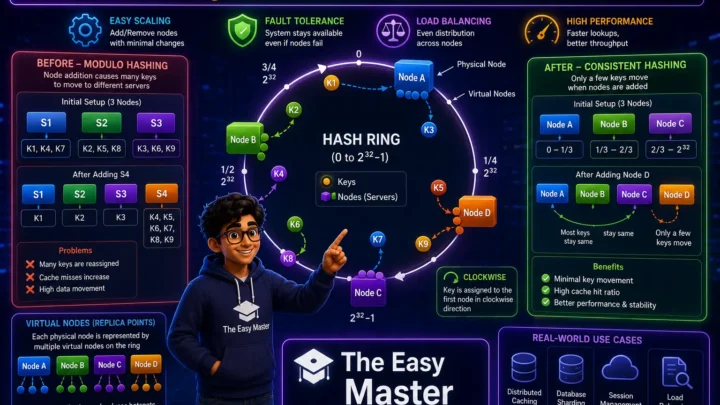
4.2 Consistent Hashing
Consistent hashing – server pool change hone par bhi only k/n keys remap hoti hain (k = keys, n = servers), not all keys।
How it works:
- Servers and keys both mapped on a hash ring (0 to 2^32-1)
- Each request key hashed, request goes to next server clockwise
- Adding or removing server affects only immediate neighbors
Visual:
        S1
       /   \
      /     \
     K1     K2
    /         \
   /           \
  K3           S2
   \           /
    \         /
     \       /
      \     /
       K4
        S3
When you add new server S4, only keys between S3 and S4 move; rest unaffected।
Pros:
- Scaling smooth – minimal cache invalidation
- Widely used in distributed caches (Redis Cluster, DynamoDB, Cassandra)
Cons:
- Implementation complexity
- Virtual nodes needed to handle server load imbalance
Use case: Distributed caching (CDN, Redis Cluster), database sharding।
4.3 URL Hash
Request ke URL ko hash karta hai – useful for CDNs, caching based on resource path।
Example: /images/logo.png hamesha same cache server pe jaayega।
5. Other Algorithms – Least Connections, Least Time, Random
5.1 Least Connections
Traffic को उस server pe bhejता है जिसके पास currently सबसे कम active connections hain।
Pros: Handles requests of varying lengths well (e.g., some requests slow, some fast)।
Cons: Requires tracking connection count per server।
Use case: Long-lived connections (WebSocket, database connections), request processing time variable।
5.2 Least Time (Least Response Time)
Response time aur connections dono ko consider karta है – server select karta है जिसके पास lowest average response time and fewest connections।
Pros: Best performance for latency-sensitive apps।
Cons: More overhead to measure response time।
5.3 Random
Randomly pick server – with enough requests, approximates round robin but simpler to implement।
Usually not used alone; random with weighting or two-choice random used sometimes।
5.4 Summary Table
| Algorithm | Basis | Best for | Sticky |
|---|---|---|---|
| Round Robin | Sequential | Equal servers, stateless | No |
| Weighted RR | Weight factor | Unequal capacities | No |
| IP Hash | Client IP | Sticky sessions without cookies | Yes |
| Consistent Hashing | Hash ring | Distributed caches, scaling | Yes |
| Least Connections | Active connection count | Long/uneven request processing | No |
6. Session Persistence (Sticky Sessions) – Kab Zaroori Hai?
Session persistence ensure karta hai ki same client के सारे requests ek hi server pe jaayein।
Kyun chahiye?
- Local in-memory sessions (req.user object)
- Upload progress tracking
- Shopping cart temporary data (not in shared DB)
- WebSocket connections
Implementations:
| Method | How it works | Pros | Cons |
|---|---|---|---|
| Cookie-based | Load balancer sets a cookie (e.g., SERVERID=3) | Simple, client controls | Cookie size, may be blocked |
| IP hash | Client IP se server select | No cookie overhead | NAT issue, imbalance |
| Application-managed | External session store (Redis) + any server | Stateless backend | Extra component, network calls |
💡 Modern approach: Avoid sticky sessions by using external session store (Redis, Memcached) or JWT tokens (client-side storage)। This way, any server can handle any request – true horizontal scaling।
Note: Sticky sessions create coupling – if server goes down, user loses session। For high availability, avoid if possible।
7. Health Checks – Dead Servers Ko Kaise Detect Karein
Load balancer regularly health checks perform karta hai to detect unhealthy servers।
Types of health checks:
| Type | Description | Example |
|---|---|---|
| Active (push) | Load balancer periodically sends probe | TCP connection, HTTP GET /health |
| Passive | LB detects failed request | After 3 consecutive failures, mark server down |
Health check parameters:
- Interval – how often to check (5-30 seconds)
- Timeout – how long to wait for response (2-5 seconds)
- Healthy threshold – consecutive passes required to mark healthy (2-3)
- Unhealthy threshold – consecutive failures to mark down (2-3)
HTTP health check example (NGINX config):
upstream backend {
    server 10.0.0.1:80 max_fails=3 fail_timeout=30s;
    server 10.0.0.2:80 max_fails=3 fail_timeout=30s;
}
Best practice: Create a simple /health endpoint that returns 200 only when app and database are ready। Use initialDelay to allow app startup time।
8. Active-Passive vs Active-Active – High Availability Modes
Load balancers themselves can be deployed in HA configurations:
| Mode | Description | Failover time | Resource utilization |
|---|---|---|---|
| Active-Passive | Ek load balancer active, doosra standby (idle) | 5-30 seconds (via keepalived) | 50% capacity idle |
| Active-Active | Dono load balancers active, traffic split (with shared VIP) | Instant (via routing table) | 100% utilization |
Most cloud load balancers (AWS ALB, GCP LB) are active-active natively। On-premise, you may use Keepalived + Virtual IP for active-passive।
Recommendation: Cloud managed load balancers use karein (AWS ALB, GCP LB, Azure LB) – automatically HA, no manual setup।
9. Real-World Examples – Nginx, HAProxy, AWS ALB
9.1 NGINX Load Balancer Configuration (Layer 7)
http {
    upstream backend_servers {
        # Load balancing algorithm (default round robin)
        least_conn;                 # or round_robin, ip_hash, random

        server 10.0.0.1:80 weight=3 max_fails=2 fail_timeout=30s;
        server 10.0.0.2:80 weight=1;
        server 10.0.0.3:80 backup;  # backup server

        # Sticky session via cookie
        sticky cookie srv_id expires=1h;
    }

    server {
        listen 80;
        server_name example.com;
        location / {
            proxy_pass http://backend_servers;
            proxy_set_header Host $host;
            proxy_set_header X-Real-IP $remote_addr;
        }
    }
}
9.2 HAProxy Configuration
haproxy
global
    log /dev/log local0

defaults
    log global
    mode http
    option httplog

frontend web_frontend
    bind *:80
    default_backend web_backend

backend web_backend
    balance roundrobin        # or leastconn, source (IP hash)
    option httpchk GET /health
    server web1 10.0.0.1:80 check weight 3
    server web2 10.0.0.2:80 check weight 2
    server web3 10.0.0.3:80 check backup
9.3 AWS Application Load Balancer (ALB)
- Layer 7 load balancer
- Listener rules – path-based, host-based routing
- Target groups – EC2 instances, Lambda, IP addresses
- Sticky sessions – enable with cookie duration
- Health checks – configurable per target group
- Auto scaling – integrates with ASG
Use case: Path-based routing to microservices:
/api/*→ API target group/static/*→ static content target group/*→ frontend target group
10. Load Balancer in Docker / Kubernetes
10.1 Docker
- Default – Docker host port mapping distributes traffic only if multiple containers on same host.
- User-defined bridge – With
--publishmode, you still need external LB (NGINX, HAProxy) for multi-host scaling. - Swarm mode – Built-in routing mesh (internal load balancer)।
10.2 Kubernetes
Kubernetes provides Service object which acts as an internal load balancer:
| Service Type | Load balancing behavior |
|---|---|
| ClusterIP | Internal LB – distributes traffic to pods within cluster |
| NodePort | Exposes service on each node’s IP at a static port, LB round robin across pods |
| LoadBalancer | Provision cloud LB (AWS, GCP, Azure) and integrates with external LB |
| Ingress | Layer 7 LB – path/host routing, SSL termination |
Kubernetes load balancing algorithms: kube-proxy uses round robin or random by default (via iptables/IPVS)。 Can configure session affinity (sessionAffinity: ClientIP)。
Example Service YAML:
apiVersion: v1
kind: Service
metadata:
  name: myapp-service
spec:
  selector:
    app: myapp
  ports:
    - port: 80
      targetPort: 8080
  type: LoadBalancer
  sessionAffinity: ClientIP
11. Common Mistakes (aur Unka Solution!)
| Mistake | Why it’s wrong | Solution |
|---|---|---|
| Not configuring health checks | Unhealthy servers still receive traffic | Configure health checks with proper thresholds |
| Using sticky sessions unnecessarily | Couples client to server, scaling issues | Use external session store (Redis) instead |
| Hardcoding load balancer IP | Single point of failure, can change | Use DNS name (cloud LB), or service discovery |
| Not setting timeouts | Slow backend ties up connections | Set connection and request timeouts |
| Ignoring SSL termination overhead | Backend servers waste CPU on SSL | Terminate SSL at load balancer, use HTTP backend |
| Using round robin for long-lived connections | Connections not balanced properly | Use least connections algorithm |
| No backup servers | All servers fail → downtime | Configure backup servers |
| Load balancer itself single point of failure | Load balancer goes down, entire app down | Use HA mode (active-passive or cloud managed) |
| Misconfigured sticky cookie domain | Cookie not sent for subdomains | Set domain attribute properly |
💡 Personal Experience: Maine ek baar health check configure karna bhool gaya – database server crash पर traffic jaata raha, users को 500 errors mil rahe the। 30 minutes lage problem identify karne mein। Ab हर load balancer configuration में mandatory health checks हैं।
12. Best Practices – Production-Level Tips
✅ Always use health checks – Without health checks, load balancer blind hai। Configure /health endpoint that checks app and dependencies।
✅ Use Layer 7 for web apps – More features (path routing, host routing, content-based switching)।
✅ Prefer least connections for variable request times – More fair than round robin when some requests take longer।
✅ Avoid sticky sessions if possible – Use shared session store (Redis) to keep backend servers stateless।
✅ Set appropriate timeouts – client_timeout, connect_timeout, server_timeout to prevent hanging requests।
✅ Use SSL termination at load balancer – Frees backend servers from TLS overhead。
✅ Enable access logs – Helps debug traffic distribution, security audits。
✅ Use geo-based routing for global apps – Route users to nearest region (AWS Route53 + LB)।
✅ Monitor load balancer metrics – Request rate, error rate, target response time, healthy host count।
✅ Implement circuit breaking / retries – Prevents cascading failures (HAProxy, Envoy support)।
✅ Test failure scenarios – Kill a server, see if LB marks it unhealthy and traffic shifts।
NGINX specific tips: Use
keepaliveconnections to reduce latency। Enablegzipcompression at LB level। Useproxy_cachefor static content caching।
13. Resources – Cheat Sheet & Practice Prompts
Load Balancing Algorithms Cheat Sheet
| Algorithm | Command / Config | Best for |
|---|---|---|
| Round Robin | balance roundrobin (HAProxy) | Equal capacity servers |
| Weighted RR | weight 3 | Unequal capacity |
| Least Connections | balance leastconn | Variable request length |
| IP Hash | ip_hash; (NGINX) | Sticky sessions |
| Consistent Hashing | hash $request_uri consistent; | Cache-friendly |
| Random | balance random | Simple distribution |
Health Check Config Snippets
NGINX:
server backend1:80 max_fails=3 fail_timeout=30s;HAProxy:
haproxy
option httpchk GET /health
server web1 10.0.0.1:80 check inter 5s rise 2 fall 3
AWS ALB: Target group → Health check settings → Path /health。
Practice Prompts
Beginner:
- Simple Node.js app likho (Express)। 2 instances run karo (different ports)। NGINX install karo and configure round robin between them।
aborcurlse test karo ki requests distribute ho rahi hain।
Intermediate:
- IP hash or cookie-based sticky sessions configure karo। Test karo ki same client hamesha same server ja raha hai। Show using server identifier (hostname / custom header)।
Advanced:
- Consistent hashing mock karo – simulate adding/removing cache servers। Count how many keys remap with consistent hashing vs simple hash (mod N)। Implement in Python or pseudocode।
14. FAQ
Q1: Round robin aur weighted round robin mein kya antar hai?
Round robin equal distribution karta hai irrespective of server capacity। Weighted round robin aap weights assign kar sakte ho – zyada weight wale server ko zyada requests।
Q2: Sticky sessions kab use karein aur kab avoid?
Use when backend stores session in-memory and you can’t change to shared store. Avoid because it hurts scalability and availability (server down = session lost)। Prefer external session store (Redis)।
Q3: IP hash consistent hashing se better kab hai?
IP hash simpler – use for small server pool (<5) that changes rarely। Consistent hashing is better for dynamic scaling (large clusters, distributed caches) because only fraction of keys move।
Q4: Load balancer ki capacity kaise decide karein?
Monitor CPU, memory, network of load balancer। For NGINX/HAProxy, a medium VM (2-4 vCPU) can handle 50k-100k requests/sec। Start small, scale if needed। Cloud LB (ALB) scales automatically।
Q5: Can load balancer route based on request content (headers, path)?
Yes – Layer 7 load balancers (NGINX, HAProxy in HTTP mode, AWS ALB) path, header, cookie, method ke basis par route kar sakte hain।
Q6: Load balancer khud single point of failure hai – kaise solve karein?
Use HA mode: active-passive with keepalived/VIP or cloud managed load balancers (AWS ALB/ELB) jo automatically redundant hain।
15. Conclusion – Ab Aapki Baari!
Bahut badhiya! Aapne aaj seekh liya:
✅ Load balancing tutorial Hindi – complete guide with algorithms
✅ Round robin, weighted round robin – basics and when to use
✅ Hashing algorithms – IP hash, consistent hashing, session persistence
✅ Least connections, least time, random
✅ Session persistence – sticky cookies, IP hash, trade-offs
✅ Health checks – active/passive, failover
✅ Active-passive vs active-active HA modes
✅ Real-world configs – NGINX, HAProxy, AWS ALB
✅ Load balancer in Docker / Kubernetes (Service, Ingress)
✅ Common mistakes, best practices
Load balancer modern scalable systems ka backbone है। Ab aap confident ho ki kaunsa algorithm kab use karna hai, aur kaise high availability achieve karni hai।
Aapki challenge: Local environment mein NGINX setup karo with two backend servers (simple HTTP servers)। Round robin test karo, phir IP hash enable karo and see difference। Apna config comment mein share karo!
Next topic kya chahiye?
- Caching Strategies – Redis, CDN, Application Caching?
- Message Queues – RabbitMQ vs Kafka?
- Database Sharding Deep Dive?
Comment mein batao!
The Easy Master ke saath load balancing seekhte raho। Happy distributing! 🚀🚦
Resources
- NGINX Load Balancing Documentation
- HAProxy Algorithms Documentation
- AWS ALB User Guide
- Consistent Hashing – Wikipedia
- Kubernetes Service and Ingress
Additional Resources
- Next.js App Router – Pages Router से क्या बदला? Complete Guide 2026
- Next.js Server Components – ‘use client’ कब और कहां Use करें
- Next.js Routing – Layouts, Dynamic Routes and Nested Routes 2026
- Next.js 16 New Features – Turbopack, Cache Components and proxy.ts
- Next.js Partial Prerendering – Static and Dynamic Content साथ में
- Next.js Authentication – JWT Session Management (App Router) 2026
- Next.js SEO – Metadata API and Image Optimization समझे 2026
- Next.js TypeScript – Full-Stack Type-Safe App कैसे बनाएं
- FastAPI Kya Hai? FastAPI Python Setup Aur Pehla API Hindi 2026
- FastAPI Path Parameters Hindi – शून्य से हीरो तक गाइड 2026
- Pydantic v2 Tutorial Hindi – Data Validation Master 2026
- FastAPI dependency injection Hindi – Code Reuse Ka Magic
- FastAPI Async Await Hindi – Non-Blocking Code 2026
- FastAPI PostgreSQL SQLModel Hindi – Async Guide 2026
- FastAPI JWT Authentication Hindi – Secure API Login
- FastAPI OpenAI Integration Hindi – AI Chatbot API 2026
- FastAPI Multi-Agent AI Hindi – LangGraph Zero to Hero
- FastAPI Deployment Hindi – Railway Zero to Hero 2026
- Docker Introduction in Hindi? Containers vs Virtual Machines
- Docker Images and Containers Hindi – Pehla Container
- Docker Compose Tutorial Hindi – Node.js + MongoDB
- Docker Volumes Networking Hindi – Data Persist कैसे करें
- Kubernetes Architecture Hindi – Pods, Nodes, Cluster
- Minikube Tutorial Hindi – Local Cluster कैसे बनाए
- Kubernetes Deployments Services Hindi – App Expose Karein
- K8s Ingress Tutorial Hindi – Domain se App Access
- Helm Kya Hai? – Kubernetes Charts Se App Deploy
- GraphQL Introduction in Hindi – REST vs GraphQL Comparison
- GraphQL Schema Tutorial Hindi – Types Queries Resolvers
- GraphQL Queries Mutations Hindi – Frontend Integration
- GraphQL Advanced Features Hindi – Fragments Aliases Variables
- Apollo Server GraphQL Node.js TypeScript Hindi – API Kaise Banaye
- Apollo Client React Hindi – GraphQL Queries Use Kaise Karein
- GraphQL Testing Supertest Hindi – Queries Mutations Test
- Integration Testing Node.js – Mock DB aur APIs Hindi
- E2E Testing Playwright – GraphQL Frontend Testing & CI/CD Hindi
- System Design Kya Hai? System Design Introduction in Hindi
- Vertical Horizontal Scaling Hindi – कब क्या Use करें
Views: 320